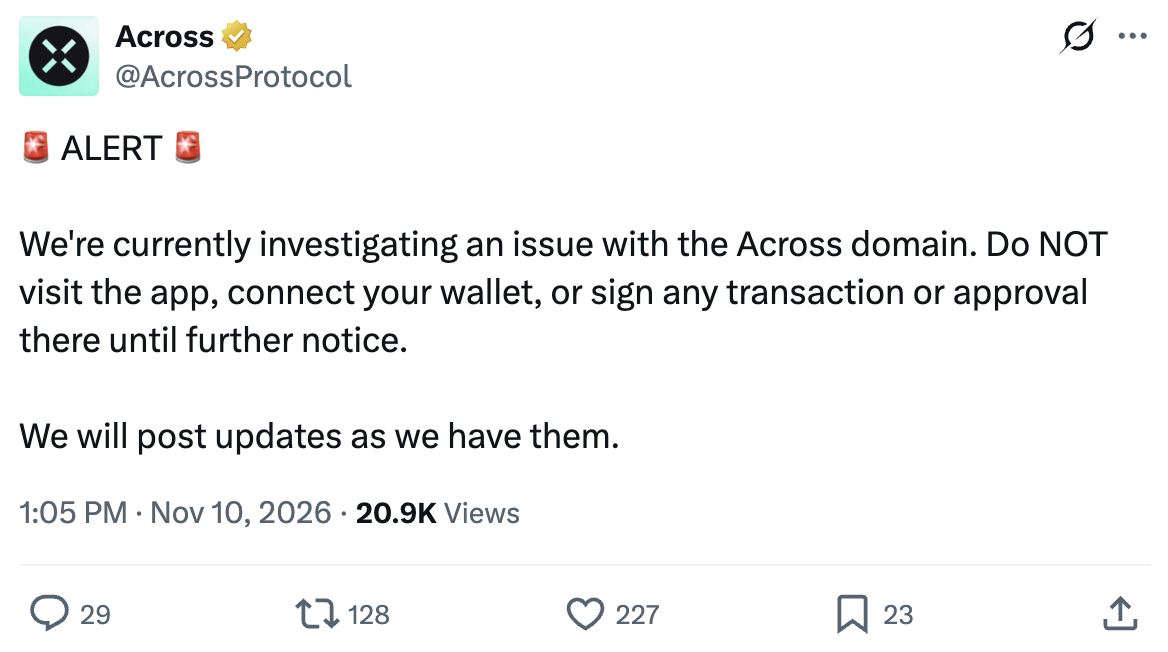
If you use Across to move assets between Ethereum and other blockchains, the immediate custody concern is whether to connect a wallet or approve a transaction. As reported by Cointelegraph on Nov. 11, 2026, at 05:24 UTC+8, Across had warned users the previous day not to access its app, connect wallets, or sign transactions or approvals until further notice while it investigated a potential security incident.
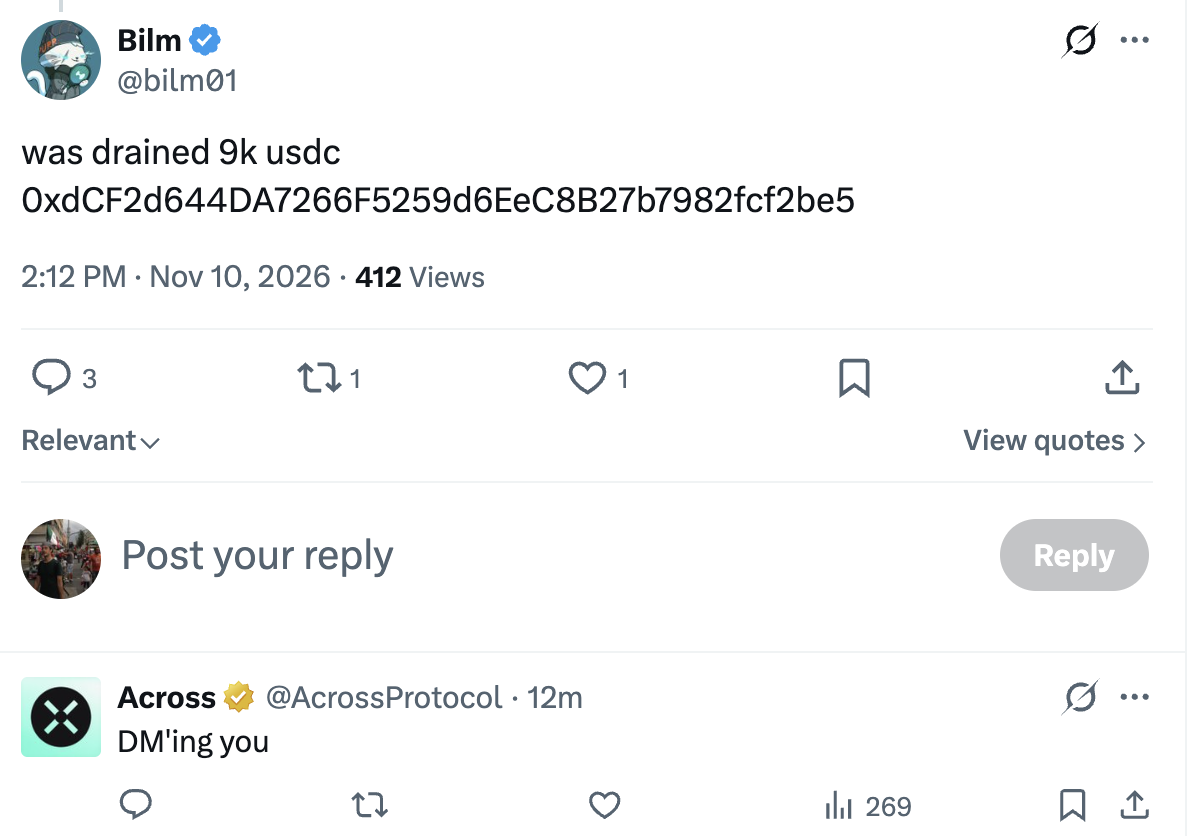
Across did not specify the nature of the incident or say whether its website had been compromised. One X user claimed to have lost $9,000 in USDC; another reported losing 7,053 USDT0 across seven transactions on Plasma. A third said their wallet was drained after using the bridge several times and alleged that the website had been compromised. Across asked the users for transaction details. Cointelegraph said it had not independently verified their reports, and Across had not immediately responded to its request for more information.
Separate NEAR AI breach
The same report described a separate incident disclosed by NEAR AI. According to its Nov. 9 incident report, attackers exploited a remote code execution vulnerability in SGLang to access an internal server and other infrastructure. NEAR AI said account details for approximately 100 users and data from 18 AI agents were exposed, including names, email addresses, agent chat histories, settings and logs; two customers had API keys exposed. It said attackers may also have observed requests processed on the compromised server, including requests in confidential mode. NEAR AI said it patched the vulnerability, revoked exposed credentials and restored access to its cloud services.
Source: cointelegraph.com (originally published 2026-11-11 05:24 UTC+8)