For someone holding assets in an Ethereum wallet, the practical question is not whether to move them today. It is how an account could remain under its owner’s control if its signature method eventually needs to change. In its November 18, 2026 discussion of Ethereum’s post-quantum plans, imToken said no quantum computer capable of breaking the relevant cryptography had yet emerged, and users did not need to rush to transfer assets.
Where the risk begins
Ethereum’s ordinary externally owned accounts use ECDSA signatures. A sufficiently capable fault-tolerant quantum computer running Shor’s algorithm could, in theory, derive a private key from an exposed public key and forge signatures without obtaining a recovery phrase or compromising a wallet app. This is a future cryptographic risk, not a reported attack or loss.
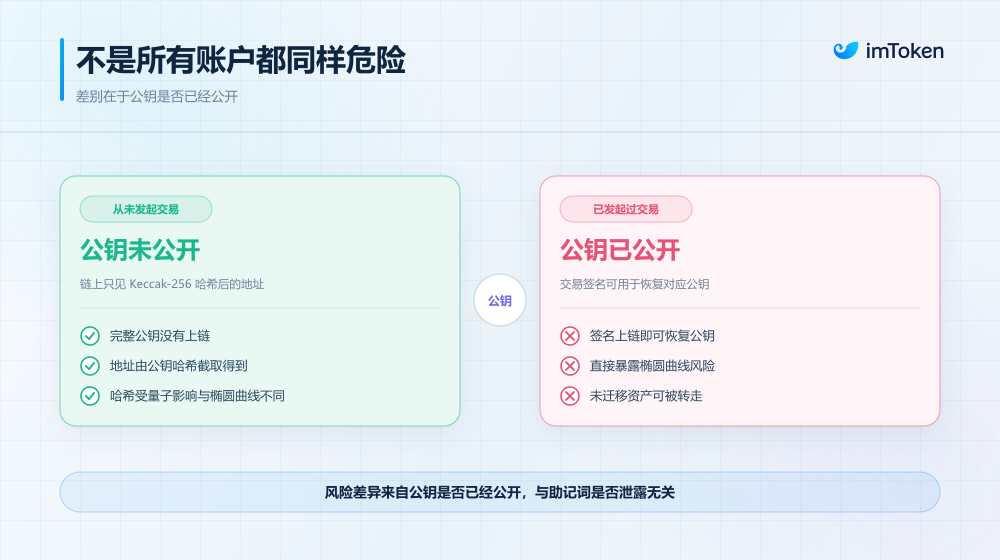
Exposure differs by account. An ordinary Ethereum address is derived by hashing a public key with Keccak-256. According to imToken, an account that has never sent an on-chain transaction or exposed a signature off-chain does not reveal its full public key through its address alone. Once it signs a transaction—including a transfer or contract authorization—the public key can be recovered from the public signature. Hash functions such as Keccak-256 are more resilient to the quantum techniques discussed here than the elliptic-curve assumptions behind ECDSA.
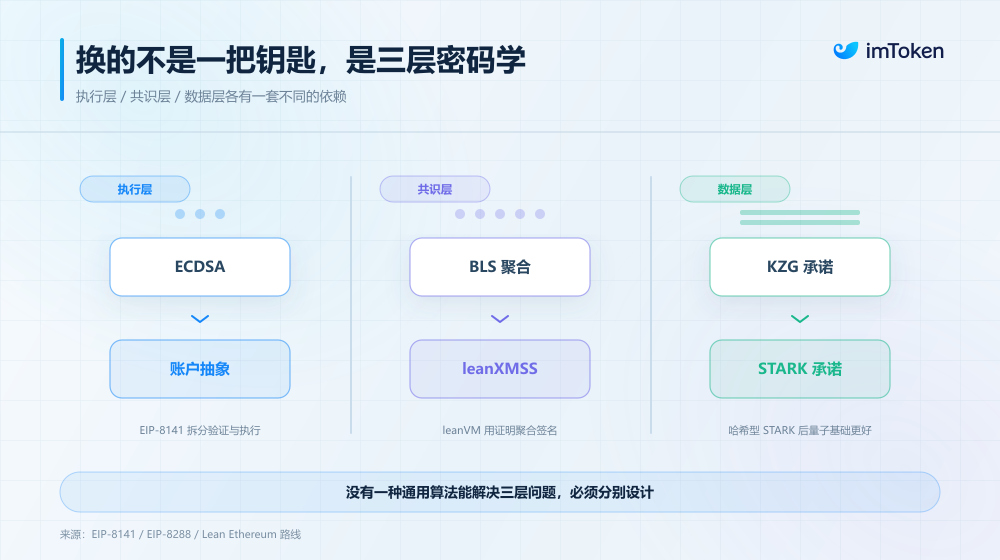
The issue also reaches beyond personal wallets. Ethereum’s proof-of-stake validators use BLS signatures, while KZG commitments support Blob and Rollup data availability. Some pairing-based zero-knowledge proofs have related long-term concerns; hash-based STARKs do not rely on the same elliptic-curve discrete-logarithm assumption.
Plans across Ethereum’s layers
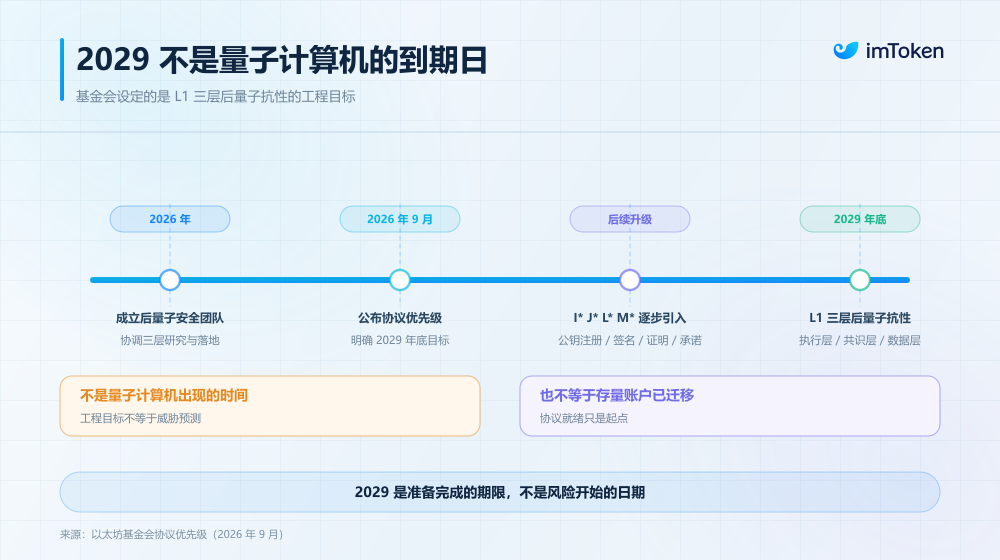
ImToken reported that the Ethereum Foundation established a Post-Quantum Security team in 2026. It said protocol priorities published in September 2026 set a target, not a completed upgrade, of making Ethereum L1 resistant to quantum attacks across its execution, consensus and data layers by December 2029.
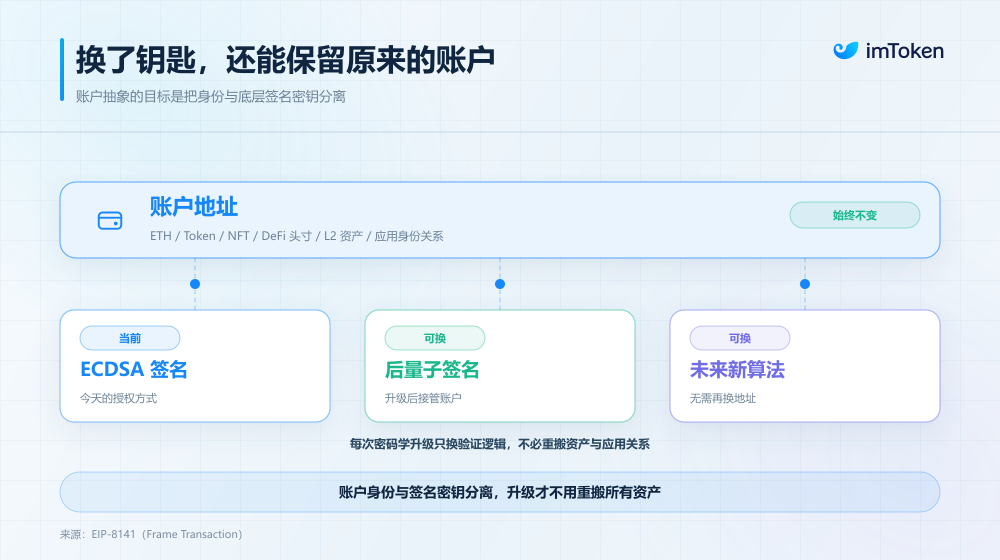
On the execution layer, proposed native account abstraction, including EIP-8141, aims to separate transaction validation, execution and gas payment. Programmable validation could eventually let an account change its signing method without necessarily changing its address. Research into post-quantum signature-verification precompiles addresses how contracts and accounts might check new signatures. EIP-8288 proposes using recursive STARK aggregation to reduce the on-chain burden of verifying larger post-quantum signatures. These are proposals and research directions, not protections that ordinary accounts already have.
On the consensus layer, the Lean Ethereum direction described by imToken considers leanXMSS, a hash-based signature approach intended to replace validators’ BLS signatures, and leanVM, an approach to aggregating such signatures into compact proofs. Replacing BLS directly would otherwise raise propagation, storage and verification costs. KZG commitments and some application-layer proofs would require attention too, so migration would extend beyond wallet signatures and Ethereum L1.
The harder wallet question: retaining control
A new key alone does not solve account migration. A conventional account using a new signing system would generally need a new address, while its existing address may hold ETH, tokens, NFTs, DeFi positions and assets on different L2 networks. Applications may also associate permissions or history with that address. Account abstraction could make it possible to change the underlying authorization method while retaining an address, but that outcome is not yet guaranteed for existing users.
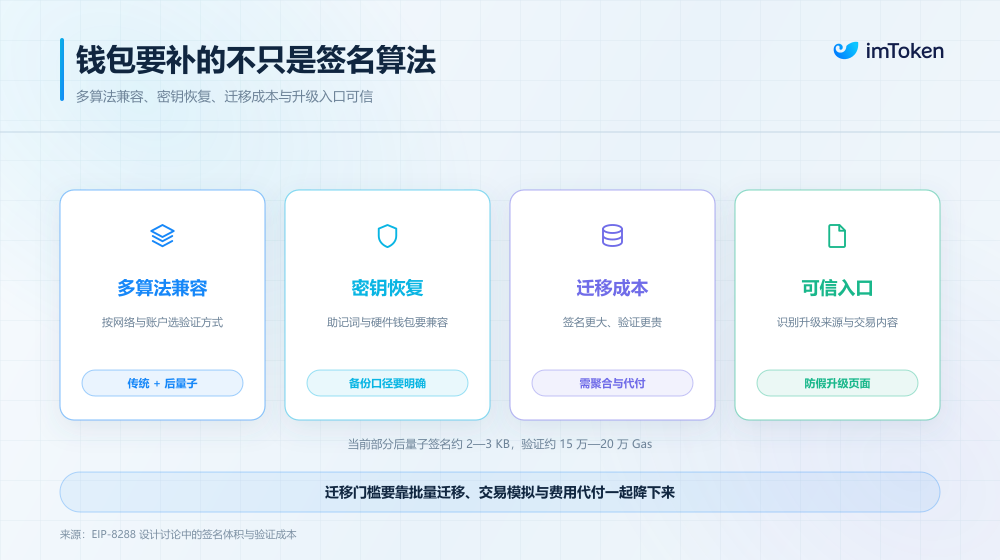
The preferable migration described by imToken would happen while the old signature method remains secure: a user would generate a new key and authorize updated account-validation rules with a valid signature from the existing account. If attackers could already forge that old signature, it would be difficult to distinguish their authorization from the owner’s. Accounts that are inactive, have lost keys or have owners unaware of an upgrade pose a separate unresolved problem. Whether any such accounts should remain unchanged or face measures such as a protocol-governed freeze remains disputed.
For holders, the immediate habit is to treat any purported “quantum-safe upgrade,” private-key check or asset-migration page with care. ImToken warns that such claims could be used to solicit recovery phrases or malicious approvals. No urgent quantum-driven transfer was warranted as of its November 18, 2026 report; any eventual migration should make the upgrade’s origin, transaction contents and resulting asset permissions clear before a user authorizes it.