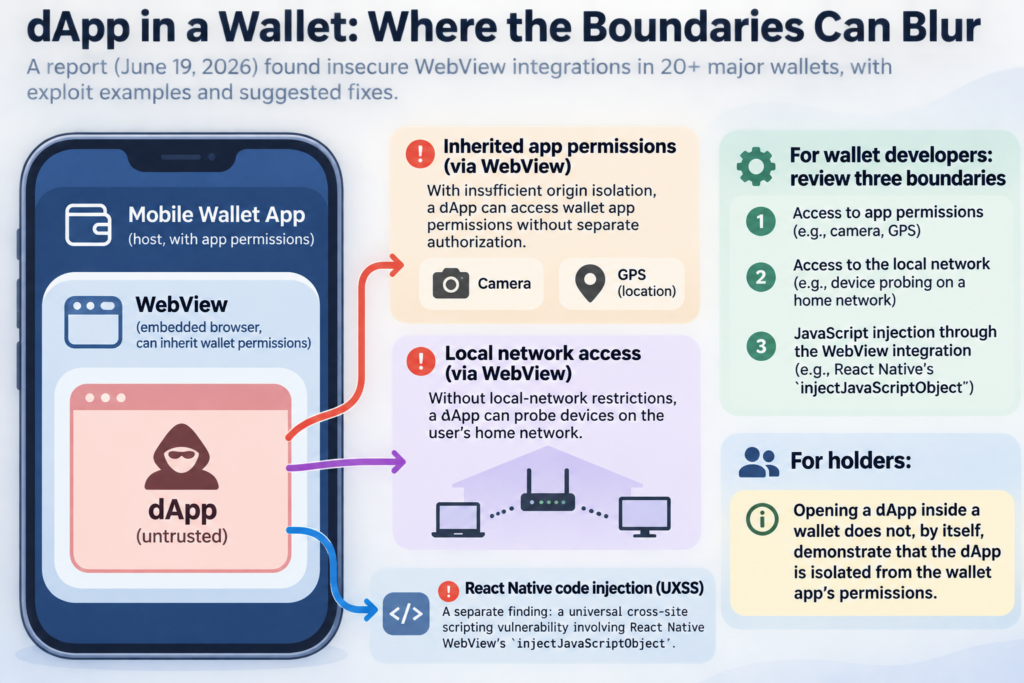
A dApp opened inside a mobile wallet may reach beyond the page a user intended to visit. In a report published on June 19, 2026, the author said they found insecure WebView integrations in more than 20 major wallets and provided exploit examples and suggested fixes. The supplied account does not name the wallets or establish that users suffered losses.
WebView can inherit permissions granted to its host wallet app. According to the author, insufficient origin isolation could let a malicious dApp access the camera or GPS without separate authorization. The author also reported that WebViews without local-network restrictions could let a dApp probe devices on a user’s home network.
A separate finding concerned a code-injection vulnerability, described as universal cross-site scripting (UXSS), involving React Native WebView’s injectJavaScriptObject.
For wallet developers, the reported findings point to three boundaries to review: access to app permissions, access to the local network, and JavaScript injection through the WebView integration. For holders, the key distinction is that opening a dApp inside a wallet does not, by itself, demonstrate that the dApp is isolated from the wallet app’s permissions.