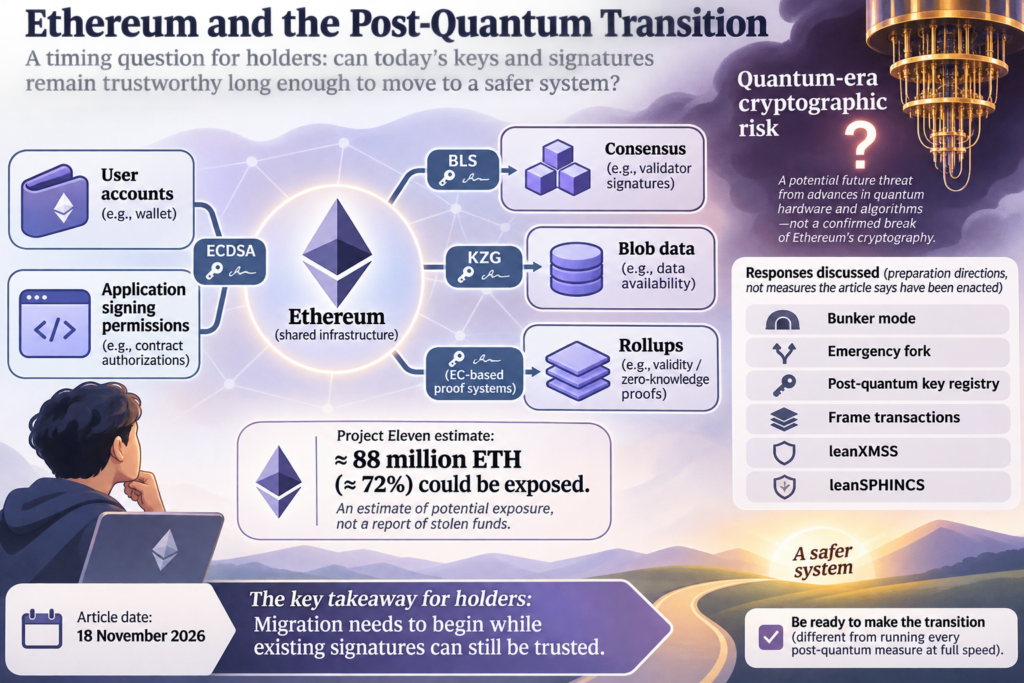
A wallet holder’s concern is whether today’s keys and signatures will remain trustworthy long enough to move to a safer system. An article published on 18 November 2026 examines that question for Ethereum. It describes advances in quantum hardware and algorithms as a potential future threat—not a confirmed break of Ethereum’s cryptography.
The article identifies several systems that could be affected: ECDSA signatures used by user accounts, application signing permissions, BLS in consensus, KZG commitments, and elliptic-curve-based proof systems used by Rollups. Blob data is also part of the risk picture. Because these systems share underlying infrastructure, the concern extends beyond any one wallet.
Citing an estimate by Project Eleven, the article says roughly 88 million ETH, or about 72%, could be exposed. That is an estimate of potential exposure, not a report of stolen funds.
The responses it discusses include a “bunker mode,” an emergency fork, a post-quantum key registry, frame transactions, and leanXMSS and leanSPHINCS. These are directions for preparation, not measures the article says have been enacted. Its central point for holders is a timing one: migration needs to begin while existing signatures can still be trusted. Being ready to make that transition is different from running every post-quantum measure at full speed.