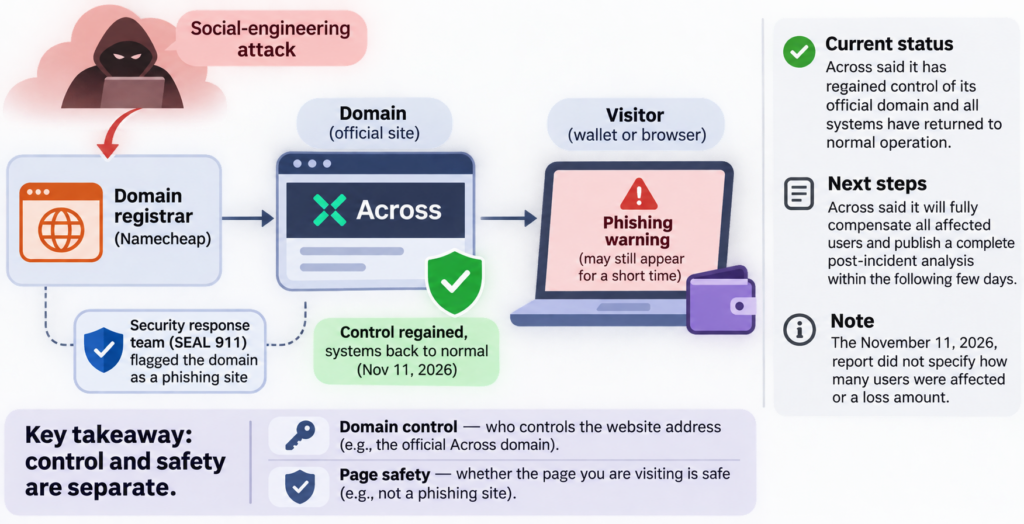
A website address is not, by itself, proof that the site behind it is safe. In a report published on November 11, 2026, cross-chain protocol Across said it had regained control of its official domain and that all its systems had returned to normal operation.
Across previously said an attacker gained control of the domain through a social-engineering attack targeting its registrar, Namecheap. While the domain was out of its control, the security response team SEAL 911 helped flag it as a phishing site, according to the report.
Across said it would fully compensate all affected users and publish a complete post-incident analysis within the following few days. The report did not state how many users were affected or give a loss amount. Across also cautioned that some wallets or browsers might continue to show phishing warnings, which it expected to clear soon.
The incident illustrates a distinction worth keeping in mind when checking a wallet connection: control of a familiar domain and the safety of the page it serves are separate questions. The promised post-incident analysis may clarify the scope of this incident; the November 11 report did not provide those details.