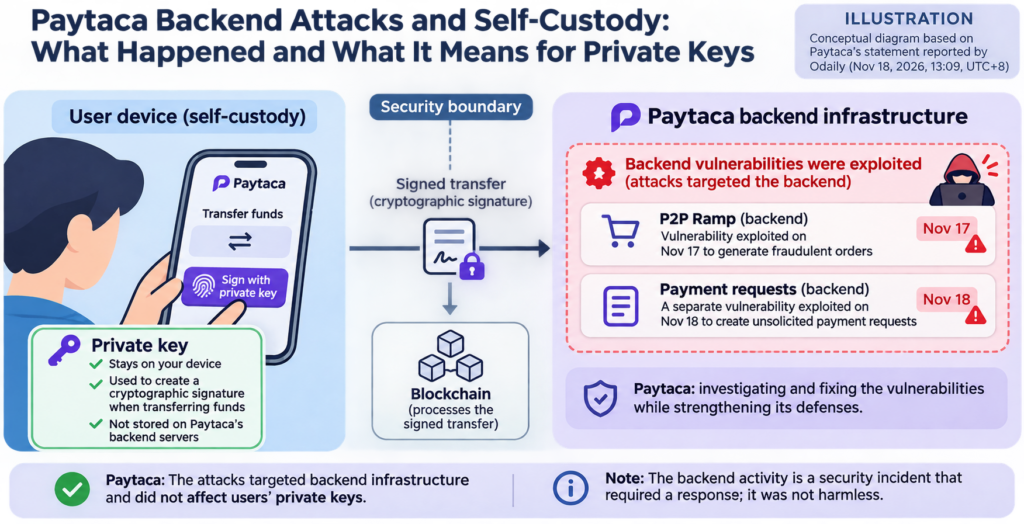
For Paytaca users, the key custody question is whether the backend attacks reached the private keys needed to move funds. In a report published on November 18, 2026, at 13:09 (UTC+8), Odaily said Paytaca had detected and responded to attacks exploiting backend vulnerabilities. Paytaca said the attacks targeted its backend infrastructure and did not affect users’ private keys.
According to Paytaca, a P2P Ramp backend vulnerability was exploited on November 17 to generate fraudulent orders. On November 18, attackers exploited a separate backend vulnerability to create unsolicited payment requests. The team said it was investigating and fixing the vulnerabilities while strengthening its defenses.
Paytaca said its self-custody design requires a cryptographic signature made with a private key to transfer funds. Those keys remain on users’ devices and are never stored on Paytaca’s backend servers, it said. That distinction explains Paytaca’s statement about the keys; it does not mean the reported backend activity was harmless.